Multi-Factor Authentication (MFA) has received increasing attention in recent months amid growing concerns over data breaches and the exposure of authentication credentials, such as usernames and passwords, which may fall into the hands of malicious actors. While leaked credentials do not necessarily mean that an organization’s entire database or all personal data has been compromised, such credentials may be exploited by fraudsters or other unauthorized persons to gain access to systems. These risks have driven significant developments in Thailand’s cybersecurity landscape. In August 2026, the Cabinet approved measures requiring password resets, reviews and management of information technology systems, and the increased adoption of MFA across government systems. These measures have since progressed towards implementation. In parallel, the Notification of the National Cyber Security Committee on Website Security Standards B.E. 2568 (2025), which came into effect on 16 September 2026, also provides for organizations to consider MFA or Digital ID, in accordance with recommendations of the Digital Government Development Agency (DGA), in addition to access control measures. MFA is therefore no longer merely a response to credential-related incidents, but is increasingly becoming part of the security measures that organizations should seriously consider implementing.
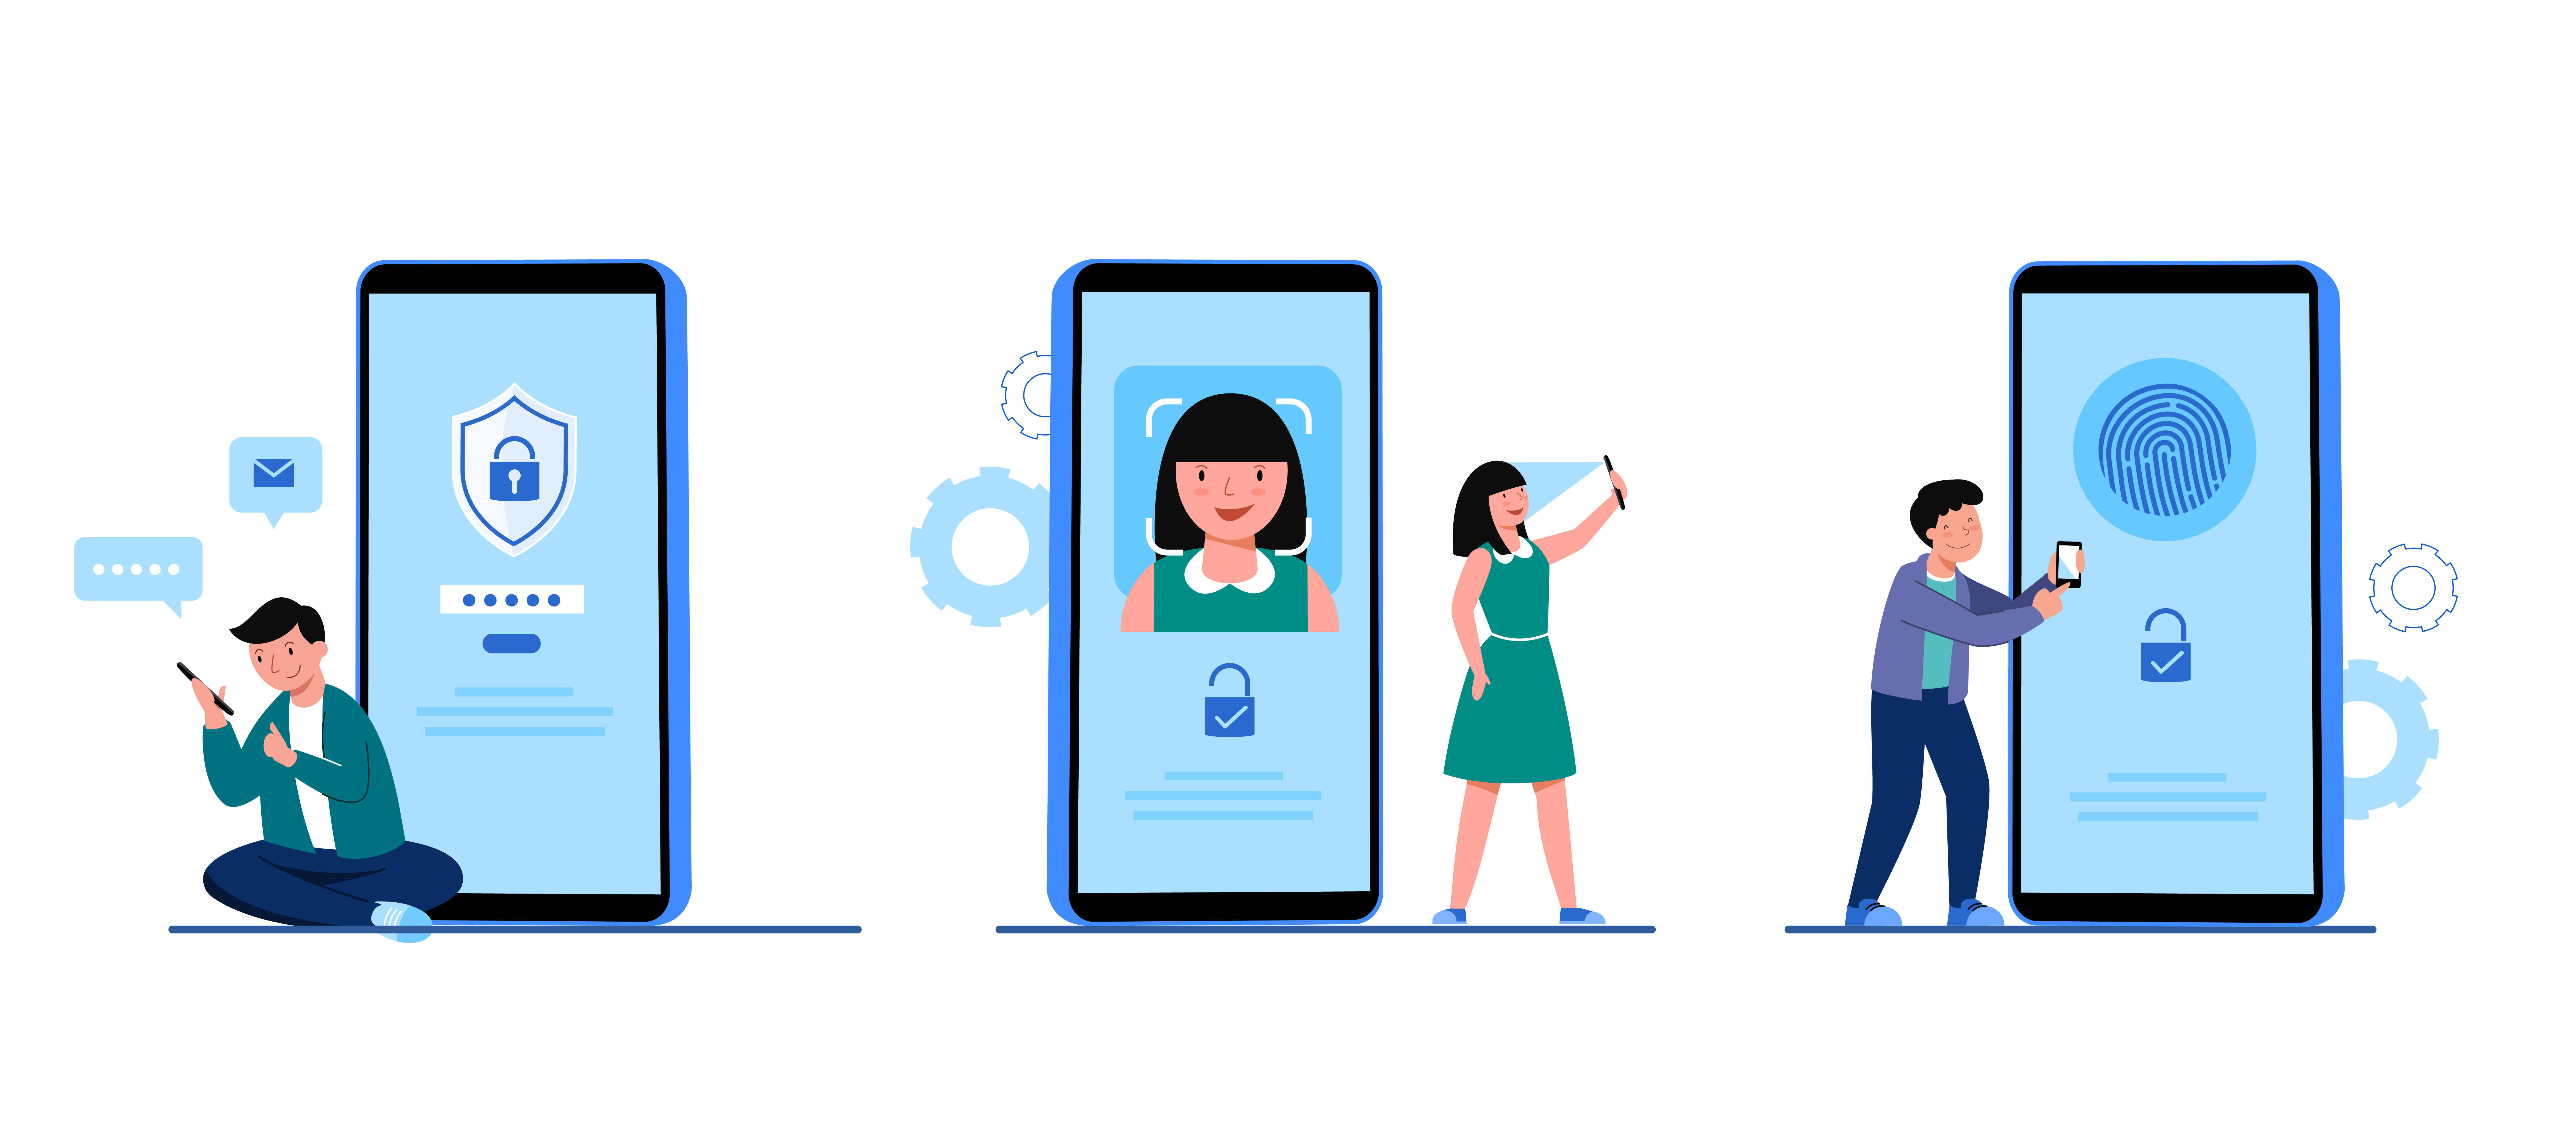
MFA is an authentication process that requires more than one type of factor before a user is granted access to a system. Instead of relying solely on a username and password, MFA adds an additional layer of authentication, such as a code generated by an authenticator application, digital identity verification, an authentication device, or biometric information. These factors generally fall into three categories: something the user “knows”, such as a password or PIN; something the user “has”, such as a mobile phone or security key; and something the user “is”, such as a fingerprint or facial recognition. By adding another authentication factor, MFA can help prevent unauthorized access even where a password has been compromised. However, different forms of MFA provide different levels of security. Organizations should therefore select an appropriate form of MFA based on the importance of the relevant system and its level of risk.
MFA is an important measure that is closely connected to personal data security under Thailand’s Personal Data Protection Act B.E. 2562 (2019) (PDPA). Under Section 37(1) of the PDPA, a data controller is required to implement appropriate security measures to prevent the loss of, or unauthorized or unlawful access to, use, alteration, modification, or disclosure of personal data. The Personal Data Protection Committee (PDPC) has also emphasized a range of security measures, including the management of passwords and authentication credentials, the use of MFA for systems that provide access to personal data, data encryption, data backup, security updates and remediation of vulnerabilities, as well as restricting access to personal data based on necessity. This reflects an important principle: effective personal data protection should not rely on any single security measure. Rather, organizations should implement appropriate and, where necessary, multiple measures to strengthen the effectiveness of personal data protection.
Although the Cabinet measures to strengthen the use of MFA primarily focus on government systems, the obligation under the PDPA to implement appropriate security measures is not limited to public-sector organizations. Both public- and private-sector data controllers should assess, based on the nature of the personal data, the relevant systems, and the level of risk, whether MFA or other authentication measures should be implemented for systems that provide access to personal data. This does not mean that the PDPA requires every organization to implement MFA across every system in the same manner. The key consideration is whether an organization can demonstrate that the security measures it has selected are appropriate to the relevant risks and provide an adequate level of protection for personal data.
From a PDPA perspective, MFA should therefore form part of an organization’s broader assessment of whether its security measures remain appropriate to the nature of the data, systems, technologies, and current level of risk. As cybersecurity practices increasingly focus on stronger authentication and access controls, organizations should look beyond simply asking, “Do we have MFA?” and instead consider, “Are our existing security measures sufficient and appropriate to the risks associated with our personal data processing activities?”
Athentic Consulting provides advisory services on personal data protection and PDPA compliance, including reviews of existing personal data processing activities to identify organizational risks and compliance gaps. We also provide data security and cybersecurity advisory services, covering measures to strengthen data security, protect against cyber threats, enhance organizational cyber readiness, and develop appropriate security improvement plans tailored to each organization’s specific context. Our aim is to help organizations move beyond compliance on paper by implementing practical measures that effectively reduce risks and strengthen the protection of personal data.
In a recent Deep Talk conversation with Krungthep Turakij, we explored the latest AI incidents making headlines worldwid...
Read More
AI risk assessment helps an organization understand what risks an AI system carries, whether it performs as expected, an...
Read More
Content is king คือคำกล่าวที่ให้ความสำคัญกับคุณภาพของเนื้อหาของสื่อประเภทต่างๆ ไม่ว่าจะอยู่ในรูปของบทความ ภาพถ่าย หรือภา...
Read More